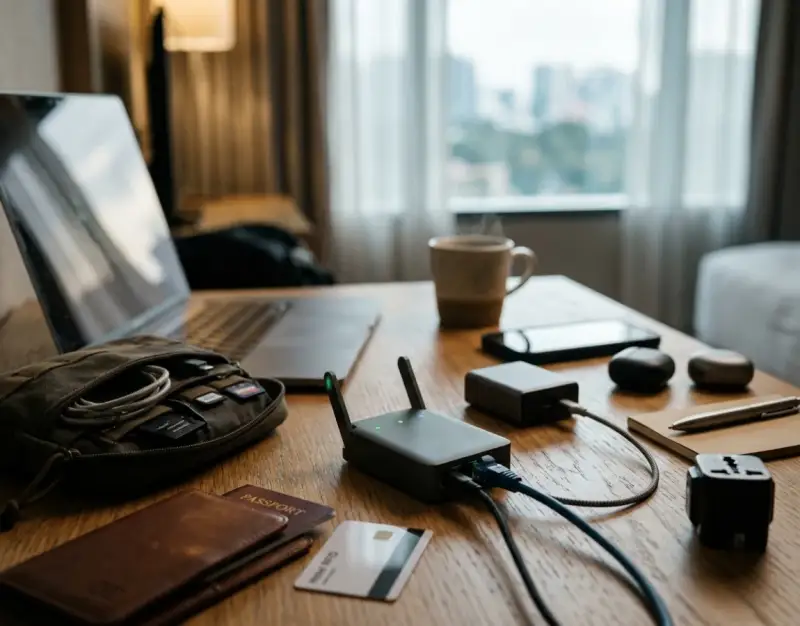
Picture this: You have just checked into a charming boutique hotel in Lisbon or a sleek high-rise Airbnb in Bangkok. You are exhausted from a twelve-hour flight, but a high-stakes client deliverable is due in precisely three hours. You open your laptop, eager to crush the deadline, only to be confronted by a glaring digital barrier: a captive portal login page that demands your room number, last name, and an excruciatingly slow terms-of-service agreement. Worse yet, once you finally navigate the digital red tape, your laptop reveals a sprawling, unencrypted public Wi-Fi network shared by hundreds of other transient guests—every single one of whom possesses a potential window into your unencrypted data packets. For the modern remote worker, this scenario is not merely an inconvenience; it is an occupational hazard of the highest order.
Over the past half-decade, the nature of remote work has undergone a seismic, irreversible evolution. The traditional office has shattered into a constellation of coffee shops, co-working spaces, airport lounges, and overseas apartments. Yet, while our offices have become infinitely more mobile, the fundamental architecture of public networking has remained dangerously archaic, fragile, and insecure. Enter the unsung hero of the modern everyday carry (EDC) kit: the compact travel router. Far more than just a niche gadget for networking enthusiasts, a dedicated portable hardware router has quietly transformed into the ultimate equalizer for digital nomads, security-conscious executives, and frequent flyers seeking absolute control over their digital environment.
In this exhaustive, master-level blueprint, we will dissect why the compact travel router has transitioned from a nice-to-have accessory to a non-negotiable cornerstone of professional digital nomad gear. We will pull back the hood on how these pocket-sized marvels operate, examine advanced deployment strategies, dismantle common configuration pitfalls, and provide a comprehensive operational framework to ensure your remote workflow remains lightning-fast, impenetrable, and bulletproof anywhere on planet Earth.
Decoding the Hardware: What Exactly is a Compact Travel Router?
To understand the utility of a compact travel router, one must first demystify what it actually is and how it fundamentally diverges from the standard wireless router sitting in your living room. At its core, a travel router is a miniature, highly specialized computing device running a customized Linux distribution—most commonly OpenWrt—engineered specifically to manage, translate, and secure network traffic on the go. Weighing often less than a deck of cards and powered by simple USB-C connections, these devices pack enterprise-grade routing capabilities into a footprint small enough to slip effortlessly into a tech pouch alongside your cables and power banks.
Unlike your laptop or smartphone, which connects directly to whatever public access point is available, a travel router acts as a sophisticated man-in-the-middle for your personal device ecosystem. When you unpack your gear in a hotel room, you instruct the travel router to connect to the venue's Wi-Fi network (or tether to your cellular smartphone). Your travel router then creates an entirely private, localized Wi-Fi network—complete with your own custom SSID and password—to which all your personal devices connect. Instead of juggling five different devices on a dodgy public network, the hotel network sees only one device: your travel router.
The Anatomy of Portable Networking: Core Components and Specifications
When shopping for high-performance digital nomad gear, navigating hardware specifications requires a discerning eye. Not all travel routers are created equal, and understanding key metrics such as CPU clock speeds, RAM allocation, and wireless standards (Wi-Fi 5 vs. Wi-Fi 6) dictates whether your device will gracefully handle heavy video conferencing or buckle under the weight of packet loss. Modern units utilize dual-band or tri-band antennas capable of broadcasting simultaneously on 2.4 GHz and 5 GHz frequencies, optimizing throughput and mitigating interference in dense urban environments.
Furthermore, look for devices that offer physical Gigabit Ethernet ports alongside high-speed wireless capabilities. Hardwiring your laptop directly into the travel router while the router bridges to a remote wireless source minimizes latency and packet jitter—a critical advantage when dealing with real-time financial trading, live streaming, or heavy software deployments. Additionally, processing power matters immensely: routing encrypted VPN tunnels at gigabit speeds demands serious computational muscle, making multi-core processors a vital feature for power users.
Understanding Client Isolation and Network Segmentation
One of the most insidious threats of public Wi-Fi is lateral movement. On a standard public network, client isolation is frequently disabled, meaning every device connected to the router can potentially "see" every other device on the subnet. If an attacker is lurking on the same coffee shop network, they can probe open ports, launch man-in-the-middle attacks, or sniff unencrypted traffic. A travel router completely neutralizes this vector by enforcing strict network segmentation. By creating an isolated local network behind a Network Address Translation (NAT) firewall, your personal devices are invisible to every other user on the host network, establishing an unbreachable digital fortress.
The Digital Nomad’s Secret Weapon: Securing Hotel and Public Wi-Fi
Public Wi-Fi networks are notoriously leaky pipes. Whether you are sipping espresso in a bustling Parisian café or logging onto a resort network in Bali, assuming privacy on an open network is an invitation for disaster. While software-based Virtual Private Networks (VPNs) offer a layer of encryption for your application traffic, they do not solve every networking headache. Software VPNs often fail to protect devices that cannot run VPN clients natively (such as smart TVs, streaming sticks, or legacy hardware), and they frequently trigger annoying CAPTCHAs or fail to bypass stubborn captive portals.
Deploying a portable wifi router running an always-on, hardware-level VPN client changes the game entirely. By flashing your router with a protocol like WireGuard or OpenVPN connected to a trusted commercial VPN provider, every single byte of data leaving your devices is encrypted *before* it ever touches the hotel's wireless infrastructure. This means the hotel network administrator, local internet service providers, or malicious actors sniffing the airwaves see nothing more than an opaque, encrypted stream of data.
Navigating Stubborn Captive Portals with MAC Cloning
Anyone who has traveled extensively knows the frustration of captive portals—those annoying web pages that pop up demanding authentication before granting internet access. These systems often lock access to a specific device’s MAC (Media Access Control) address. If you connect your laptop, log in, and later want to connect your tablet or partner's laptop, you are forced through the cumbersome authentication ritual all over again.
Advanced travel routers feature a brilliant workaround known as MAC address cloning or web UI captive portal bypass. You can use your travel router to capture the captive portal page, authenticate once via your router's interface, and seamlessly share that single authorized connection across your entire device ecosystem. Some routers even allow you to clone your laptop's MAC address directly onto the travel router, tricking the hotel network into thinking your router is your primary workstation.
Beating Throttling and Bandwidth Restrictions
Many hotels, airports, and cruise ships utilize aggressive Quality of Service (QoS) rules and deep packet inspection (DPI) to throttle bandwidth-heavy applications like video streaming, peer-to-peer file sharing, or large cloud backups. By routing all your traffic through an encrypted VPN tunnel hosted on your travel router, DPI engines lose the ability to inspect the contents of your packets. While this does not magically increase a genuinely slow internet connection, it frequently prevents automated throttling algorithms from artificially choking your connection speeds based on traffic categorization.
Step-by-Step Strategic Blueprint: Configuring Your Travel Router for Maximum Performance
Acquiring top-tier digital nomad gear is only half the battle; proper configuration is what separates amateur setups from professional-grade mobile infrastructure. Below is an exhaustive, step-by-step methodology to configure your travel router for optimal security, speed, and reliability before you ever leave home.
Step 1: Initial Unboxing, Firmware Flashing, and Hardening
Never deploy a networking device straight out of the box without auditing its software. Begin by connecting your travel router to your computer via an Ethernet cable or its default open Wi-Fi network. Navigate to the router's local IP address (typically 192.168.8.1) to access the administrative dashboard. Your absolute first priority is updating the firmware to the absolute latest stable release provided by the manufacturer or the open-source OpenWrt community.
Once updated, immediately change the default administrative password to a robust, high-entropy passphrase generated by a reputable password manager. Disable remote management entirely so that the administration panel can only be accessed locally over a wired connection or an explicitly trusted wireless SSID. Finally, change the default IP subnet of your router (e.g., changing it from 192.168.8.x to something less common like 10.42.x.x) to avoid IP routing conflicts when connecting to enterprise or hotel networks that utilize default subnets.
Step 2: Integrating Enterprise-Grade VPN Protocols (WireGuard)
Speed and security are often locked in a zero-sum game, but modern protocols have dramatically shifted the balance. When configuring your travel router, bypass older, computationally heavy protocols like OpenVPN whenever possible in favor of WireGuard. WireGuard offers state-of-the-art cryptography with a fraction of the codebase, resulting in lightning-fast connection speeds, minimal CPU overhead, and virtually unnoticeable latency inflation.
- Log into your trusted commercial VPN provider's subscriber portal and generate a manual WireGuard configuration file (.conf) or public/private key pair tied to a high-speed server location near your physical destination.
- Navigate to your travel router's VPN dashboard (often found under "VPN Client" or "WireGuard Client").
- Upload the configuration file or manually input the endpoint address, public key, allowed IPs (set to 0.0.0.0/0), and your assigned private client IP address.
- Enable the "Kill Switch" feature. This is non-negotiable: a hardware-level kill switch ensures that if your VPN connection drops unexpectedly, all internet traffic is instantly severed, preventing your real IP address or unencrypted data from leaking onto the hotel network.
- Toggle the WireGuard client to "Active" and verify your new public IP address using an external lookup tool like ipleak.net.
Step 3: SSID Stealth and Custom Wireless Optimization
Broadcast hygiene is a critical yet frequently overlooked aspect of digital hygiene. By default, your travel router may broadcast a flashy SSID like "GL-AR750-Travel-Router," practically painting a target on your back for curious onlookers or tech-savvy adversaries in a co-working space. Customize your SSID to something completely innocuous or entirely unmemorable.
Furthermore, dive into the wireless settings and optimize your channel selection and channel width. In crowded urban areas, the 2.4 GHz spectrum is almost universally congested with extreme interference from Bluetooth devices, microwaves, and neighboring routers. Force your important devices onto the 5 GHz band, utilize a channel width of 20 MHz or 40 MHz rather than 80 MHz to maximize signal stability through thick hotel walls, and disable WPS (Wi-Fi Protected Setup) to eliminate a notoriously vulnerable brute-force attack vector.
Step 4: Implementing Multi-WAN Failover and Cellular Tethering
Reliable internet is the lifeblood of the digital nomad. Relying entirely on a single hotel Wi-Fi connection is an operational gamble. Advanced travel routers support multi-WAN failover, allowing you to blend multiple internet sources into a resilient, self-healing pipeline.
Connect your smartphone to the travel router via a USB-C cable and enable USB Tethering in your phone's operating system settings. Configure your travel router to prioritize the hotel Wi-Fi as your primary WAN source, with your smartphone's cellular data designated as the automatic secondary backup. If the hotel internet crashes, experiences catastrophic latency spikes, or demands an impossible captive portal re-authentication, your travel router instantly and seamlessly switches over to your cellular data stream without dropping a single active Zoom call or data transfer.
Step 5: Establishing Ad-Blockers and Network-Wide DNS Filtering
Unsecured public networks are notorious breeding grounds for injected advertisements, tracking scripts, and malicious DNS redirects. Modern travel routers running customized firmware allow you to install and configure network-wide ad-blocking and privacy suites such as AdGuard Home or Pi-hole directly onto the router hardware.
By routing all DNS requests through a local instance running on your travel router, you strip out advertisements, trackers, and malicious domains before they ever reach your laptop or phone. This not only dramatically accelerates web page load times and slashes cellular data consumption when tethering, but it adds an extra layer of proactive threat intelligence that blocks phishing domains and known malware distribution nodes at the network layer.
Real-World Case Studies & Scenarios: Success vs. Failure
To truly grasp the value proposition of a compact travel router, examining real-world deployment scenarios illustrates the profound difference between proactive preparation and reactive vulnerability.
Scenario A: The Digital Nomad in Chiang Mai (The Resilient Workflow)
Marcus, a senior software architect and full-time digital nomad, sets up his portable workstation in a popular co-working hub in Chiang Mai, Thailand. The hub's public Wi-Fi is notoriously unstable during peak afternoon hours, frequently kicking clients off and forcing them through a tedious re-authentication portal every forty-five minutes. Furthermore, local network sniffing tools reveal that unencrypted traffic is easily readable across the shared subnet.
Marcus unpacks his pocket-sized travel router, plugs it into a portable power bank, and connects it to the co-working space's Wi-Fi network. His laptop, tablet, and work phone are permanently paired to his personal, hidden travel router SSID. His travel router maintains an unbreakable WireGuard tunnel to a secure server in Singapore. When the co-working space's Wi-Fi hiccups, Marcus’s router automatically fails over to his 5G cellular hotspot tethered via USB-C, ensuring zero dropped packets during a critical code deployment. Marcus completes his workday stress-free, completely insulated from public network vulnerabilities and captive portal fatigue.
Scenario B: The Compromised Executive in London (The Avoidable Disaster)
Sarah, a corporate vice president of strategy, travels to London for a high-profile merger and acquisition negotiation. Operating on a tight schedule, she connects her corporate laptop directly to the open, unsecured Wi-Fi network of her luxury hotel without a VPN or travel router. Unbeknownst to her, a threat actor has deployed a malicious "Evil Twin" wireless access point mimicking the hotel's legitimate SSID.
Because Sarah's laptop treats the open network as trusted, her unencrypted email syncs, cleartext HTTP traffic, and vulnerable legacy applications are immediately intercepted by the attacker. Within hours, proprietary merger documents are exfiltrated, resulting in a catastrophic compliance breach and immense financial fallout. Had Sarah utilized a travel router enforcing an encrypted hardware VPN and a strict kill switch, the malicious Evil Twin attempt would have been utterly neutralized, as the router would have refused to establish a handshake with an untrusted, unverified upstream gateway.
| Networking Approach | Security Level | Captive Portal Handling | Device Ecosystem Management | VPN & Kill Switch Integration |
|---|---|---|---|---|
| Direct Public Wi-Fi Connection | Extremely Low (Vulnerable to sniffing & MITM) | Manual login required for every single device | Chaotic (Every device exposes its own MAC address) | Dependent on software clients per device (often fails) |
| Software VPN on Laptop Only | Moderate (Encrypts app traffic, leaks DNS/metadata) | Tedious juggling of connection states | Protects only the laptop; other devices exposed | Vulnerable to OS-level leaks and app crashes |
| Compact Travel Router (EDC Setup) | Maximum (Hardware-level encryption, zero trust) | Single login handles all downstream devices | Flawless (All devices share one secure tunnel) | Always-on router-level WireGuard with absolute Kill Switch |
Critical Mistakes and How to Avoid Them
Even seasoned travelers and tech enthusiasts occasionally stumble when deploying advanced networking gear. Avoiding these five catastrophic mistakes ensures your portable infrastructure remains rock-solid.
Mistake 1: Neglecting to Update Default Administrative Credentials
The single most common and preventable security blunder is leaving a travel router on its default factory username and password (e.g., admin / password). Many travelers assume that because a travel router is a mobile device, it is immune to automated botnet scanning. If your router is broadcasting an open setup network or connected to a compromised local subnet with default credentials exposed, an attacker can easily pivot into your device's administration panel. Countermeasure: Always change administrative credentials during the initial unboxing phase and store them securely in a password manager.
Mistake 2: Failing to Enable the Hardware/Software VPN Kill Switch
Relying on a VPN connection without an active kill switch is akin to driving a car with faulty brakes while navigating a steep mountain pass. If your hotel's internet connection drops momentarily or flickers, your travel router may briefly revert to sending unencrypted traffic directly through the public gateway before re-establishing the VPN tunnel. Countermeasure: Always configure and verify your router's built-in kill switch or firewall drop rules, ensuring that zero packets can leave the device unless they are securely encapsulated within the VPN tunnel.
Mistake 3: Ignoring Local Wi-Fi Spectrum Interference
Plugging in a travel router and expecting it to instantly blast through thick concrete hotel walls on a congested 2.4 GHz channel is a recipe for catastrophic packet loss and abysmal speeds. Countermeasure: Always survey the local wireless environment using a Wi-Fi analyzer tool on your phone, force your travel router onto a clean 5 GHz channel, and position the router near a window or in line-of-sight when possible.
Mistake 4: Overloading Underpowered Hardware with Heavy VPN Encryption
Attempting to run resource-intensive cryptographic protocols like OpenVPN on a budget travel router equipped with a weak, single-core processor will choke your throughput down to a crawl, rendering high-definition video calls and large file transfers utterly impossible. Countermeasure: Invest in modern hardware featuring dedicated cryptographic acceleration chips and lightweight protocols like WireGuard.
Mistake 5: Traveling Without Offline Administrative Documentation
Finding yourself stranded in a remote location with a travel router that has entered a boot loop or locked you out of its admin panel due to a misconfiguration—with no internet access to search for troubleshooting guides—is a digital nomad's worst nightmare. Countermeasure: Always save local PDF copies of your travel router's user manual, configuration backups, and default IP reset procedures directly to your laptop's local hard drive before embarking on your journey.
Frequently Asked Questions (FAQ)
Do I really need a compact travel router if my laptop already has a VPN installed?
Yes. While a software VPN protects the specific application traffic running on your laptop, it does nothing for IoT devices, streaming sticks, or your partner's devices. Furthermore, a software VPN cannot bypass stubborn hotel captive portals, nor does it protect you from local network sniffing vectors that target unencrypted metadata, DNS queries, or unpatched operating system vulnerabilities. A travel router secures your entire device ecosystem with a single hardware-level tunnel, acting as an impenetrable perimeter defense.
Will a travel router slow down my internet speed?
It depends entirely on the hardware specifications of the router and the encryption protocol you utilize. Older routers running heavy OpenVPN protocols may experience throughput bottlenecks due to CPU limitations. However, modern travel routers equipped with multi-core processors running lightweight WireGuard protocols can easily push hundreds of megabits per second, often matching or exceeding the raw speed of the host hotel's internet connection while adding virtually zero noticeable latency.
Can I use a travel router with mobile cellular data instead of hotel Wi-Fi?
Absolutely. In fact, many advanced digital nomads rely on cellular tethering as their primary or secondary internet source. By connecting an LTE/5G smartphone or a dedicated mobile hotspot via USB tethering to your travel router, you can distribute a secure, private Wi-Fi network to all your devices using cellular data. This is exceptionally useful when working from trains, remote nature reserves, or areas with notoriously untrustworthy public Wi-Fi infrastructure.
Are travel routers difficult to set up for non-technical users?
Not at all. While networking enthusiasts can dive deep into custom OpenWrt command-line configurations, modern travel routers designed for everyday carry come equipped with exceptionally polished, user-friendly web dashboards and mobile companion apps. Most devices can be unboxed, configured with a VPN, and fully operational in less than ten minutes following straightforward graphical setup wizards.
How do travel routers handle captive portals in hotels and airports?
Travel routers handle captive portals brilliantly through a feature called MAC cloning or web UI redirection. When your travel router connects to a hotel network with a captive portal, your router intercepts the redirect. When you attempt to browse any website on your laptop, the router pulls up the hotel's login page. Once you authenticate through the router's interface, the hotel network recognizes the router's connection, granting uninterrupted internet access to all devices safely sequestered behind your private local network.
Strategic Roadmap & Final Takeaway
As we look toward the next two to five years, the intersection of remote work, global mobility, and cybersecurity will only grow increasingly fraught with complexity and risk. Public Wi-Fi networks will remain lucrative hunting grounds for cybercriminals, and the administrative friction of captive portals and bandwidth throttling will continue to plague travelers worldwide. Relying on makeshift security measures or unprotected device configurations is no longer an option for serious professionals.
Integrating a high-performance compact travel router into your everyday carry kit is the ultimate manifestation of digital self-reliance. By establishing an unbreakable hardware perimeter, enforcing absolute network segmentation, and automating seamless failovers between hotel Wi-Fi and cellular tethering, you transform any hostile public space into a sovereign, secure digital workspace. Visit Trwen Store today to explore our curated selection of elite digital nomad gear and secure your portable networking infrastructure for the adventures ahead.
Be the first to share a gentle reflection on this story.